
Weekend Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: big75certs

NSE7_CDS_AR-7.6 Leak Questions

Fortinet NSE 7 - Public Cloud Security 7.6.4 Architect Questions and Answers

Question 17

Refer to the exhibit.
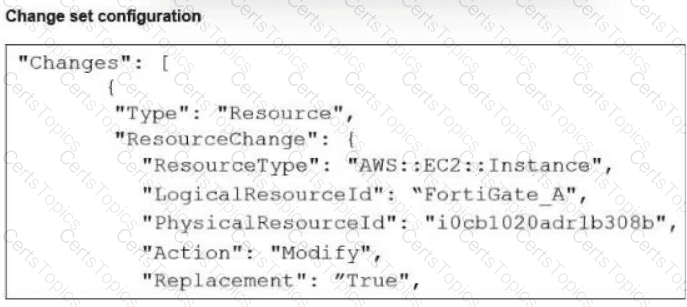
An AWS administrator created a change set to examine the effects of proposed changes to the current infrastructure.

Based only on the output shown in the exhibit, what will happen if the administrator applies these changes?

Options:

A.

The resulting FortiGate instance will lose its current local users.

B.

The deployment will take place without any service interruption.

C.

The PhysicalResourceId will remain the same.

D.

CloudFormation will roll back the current stack before updating it.

Question 18

You are experiencing intermittent connectivity issues in a FortiGate HA cluster deployed with Azure gateway load balancer. Traffic is being dropped when it passes through the cluster. What is the cause of the issue? (Choose one answer)1

Options:

A.

The FortiGate firewalls are using the default maximum transmission unit (M2TU) size supported by Azure.

B.

The Azure gateway load balancer is configured with an incorrect health probe port.

C.

The Azure gateway load balancer is blocking large packets, causing traffic failures.

D.

The protected VMs are running an application that fragments packets.

Question 19

Which statement about Transit Gateway (TGW) in Amazon Web Services (AWS) is true?

Options:

A.

Both the TGW attachment and propagation must be in the same TGW route table.

B.

TGW can have multiple TGW route tables.

C.

A TGW attachment can be associated with multiple TGW route tables.

D.

The TGW default route table cannot be disabled.

Question 20

You must add an Amazon Web Services (AWS) network access list (NACL) rule to allow SSH traffic to a subnet for temporary testing purposes. When you review the current inbound and outbound NACL rules, you notice that the rules with number 5 deny SSH and telnet traffic to the subnet.

What can you do to allow SSH traffic?

Options:

A.

You do not have to create any NACL rules because the default security group rule automatically allows SSH traffic to the subnet.

B.

You must create a new allow SSH rule anywhere in the network ACL rule base to allow SSH traffic.

C.

You must create two new allow SSH rules, each with a number bigger than 5.

D.

You must create two new allow SSH rules, each with a number smaller than 5.
