Weekend Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: big75certs

Fortinet Network Security Expert NSE7_CDS_AR-7.6 Fortinet Study Notes

Fortinet NSE 7 - Public Cloud Security 7.6.4 Architect Questions and Answers

Question 9

Refer to the exhibit.
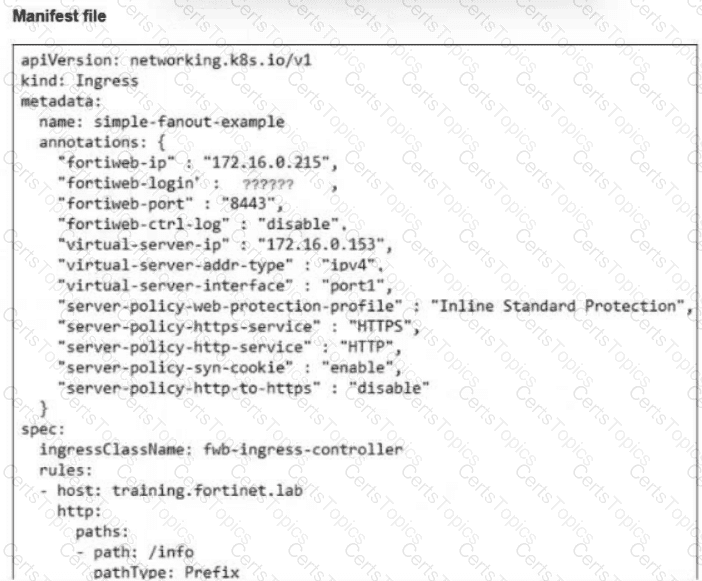
A team of AWS administrators is in the process of installing a FortiWeb ingress controller to protect containerized web applications in an Amazon Elastic Kubernetes Service (EKS) cluster. While customizing the manifest file shown in the exhibit, they realize that they do not know the correct value to enter in the fortiweb-login field.

How can they determine the correct value for this field?

Options:

A.

The correct value is the password of the FortiWeb admin account.

B.

They can find the expected value in the manifest file used to deploy the pods.

C.

They must create a Kubernetes secret with the kubectl command.

D.

They can refer to the output of the EKS cluster deployment.

Question 10

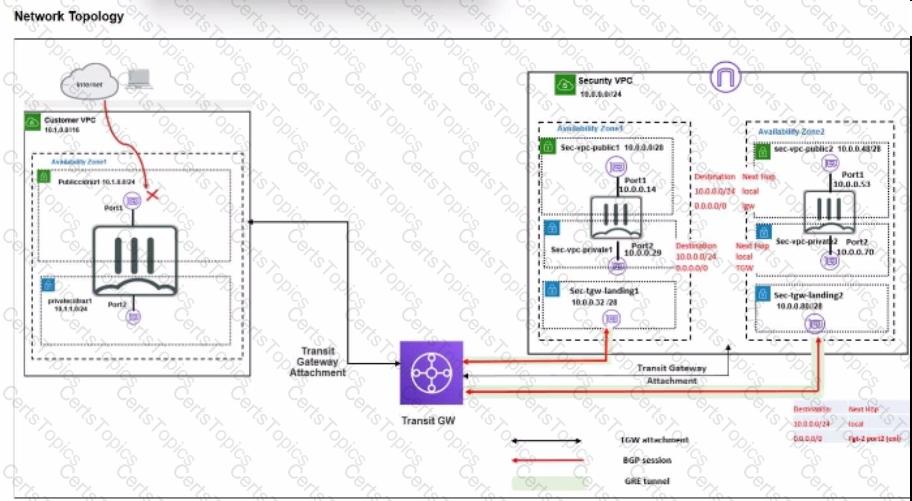
Refer to the exhibit.

In your Amazon Web Services (AWS), you must allow inbound HTTPS access to the Customer VPC FortiGate VM from the internet. However, your HTTPS connection to the FortiGate VM in the Customer VPC is not successful.

Also, you must ensure that the Customer VPC FortiGate VM sends all the outbound Internet traffic through the Security VPC.

How do you correct this issue with minimal configuration changes? (Choose three.)

Options:

A.

Add a route with your local internet public IP address as the destination and the internet gateway as the target.

B.

Add a route with your local internet public IP address as the destination and the transit gateway as the target.

C.

Add a route to the destination 0.0.0.0/0 with the transit gateway as the target.

D.

Deploy an internet gateway, associate an EIP with the Customer VPC private subnet, and then add a new route with destination 0.0.0.0/0 with the internet gateway as the target.

E.

Deploy an internet gateway, attach it to the Customer VPC, and then associate an EIP with the port1 of the FortiGate in the Customer VPC.

Question 11

As part of your organization ' s monitoring plan, you have been tasked with obtaining and analyzing detailed information about the traffic sourced at one of your FortiGate EC2 instances.

What can you do to achieve this goal?

Options:

A.

Use AWS CloudTrail to capture and then examine traffic from the EC2 instance.

B.

Create a virtual public cloud (VPC) flow log at the network interface level for the EC2 instance.

C.

Add the EC2 instance as a target in CloudWatch to collect its traffic logs.

D.

Configure a network access analyzer scope with the EC2 instance as a match finding.

Question 12

An administrator is trying to implement FortiCNP with Microsoft Azure Security integration. However, FortiCNP is not able to extract any cloud integration data from Azure; therefore, real-time cloud security monitoring is not possible.

What is causing this issue?

Options:

A.

The organization is using a free Azure AD license.

B.

The Azure account doesn ' t have the global administrator role.

C.

The administrator enabled the wrong defender plan for servers.

D.

The FortiCNP account in Azure has the Storage Blob Data Reader role.