A DLP administrator is checking the System Overview in the Enforce management console, and all of the detection servers are showing as “unknown”. The Vontu services are up and running on the detection servers. Thousands of .IDC files are building up in the Incidents directory on the detection servers. There is good network connectivity between the detection servers and the Enforce server when testing with the telnet command.
How should the administrator bring the detection servers to a running state in the Enforce management console?
Which two factors are common sources of data leakage where the main actor is well-meaning insider? (Choose two.)
What should an administrator do if DLP policies are generating too many false positives?
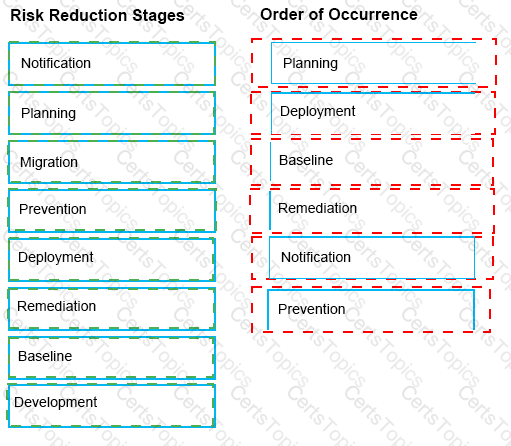
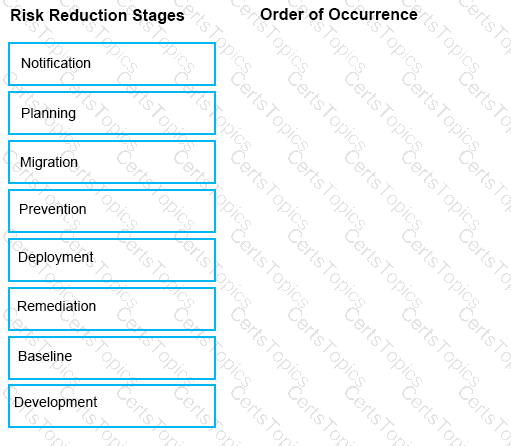
The Symantec Data Loss risk reduction approach has six stages.
Drag and drop the six correct risk reduction stages in the proper order of Occurrence column.
Copyright © 2021-2026 CertsTopics. All Rights Reserved