Pre-Winter Sale 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: save70

250-587 Exam Dumps : Symantec Data Loss Prevention 16.x Administration Technical Specialist

PDF
250-587 pdf
 Real Exam Questions and Answer
 Last Update: Sep 22, 2026
 Question and Answers: 108 With Explanation
 Compatible with all Devices
 Printable Format
 100% Pass Guaranteed
$25.5  $84.99
250-587 exam
PDF + Testing Engine
250-587 PDF + engine
 Both PDF & Practice Software
 Last Update: Sep 22, 2026
 Question and Answers: 108
 Discount Offer
 Download Free Demo
 24/7 Customer Support
$40.5  $134.99
Testing Engine
250-587 Engine
 Desktop Based Application
 Last Update: Sep 22, 2026
 Question and Answers: 108
 Create Multiple Test Sets
 Questions Regularly Updated
  90 Days Free Updates
  Windows and Mac Compatible
$30  $99.99

Verified By IT Certified Experts

CertsTopics.com Certified Safe Files

Up-To-Date Exam Study Material

99.5% High Success Pass Rate

100% Accurate Answers

Instant Downloads

Exam Questions And Answers PDF

Try Demo Before You Buy

Certification Exams with Helpful Questions And Answers

Symantec Data Loss Prevention 16.x Administration Technical Specialist Questions and Answers

Question 1

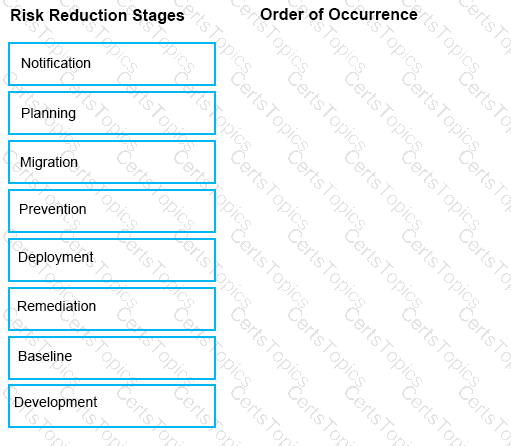
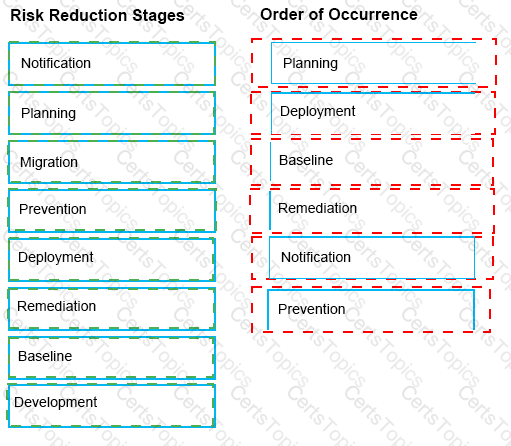
The Symantec Data Loss risk reduction approach has six stages.

Drag and drop the six correct risk reduction stages in the proper order of Occurrence column.

Options:

Buy Now
Question 2

A DLP administrator is preparing to install Symantec DLP and has been asked to use an Oracle database provided by the Database Administration team.

Which SQL *Plus command should the administrator utilize to determine if the database is using a supported version of Oracle?

Options:

A.

select database version from < database name > ;

B.

select * from db$version;

C.

select * from v$version;

D.

select db$ver from < database name > ;

Question 3

A DLP administrator determines that the \SymantecDLP\Protect\Incidents folder on the Enforce server contains. BAD files dated today, while other. IDC files are flowing in and out of the \Incidents directory. Only .IDC files larger than 1MB are turning to .BAD files.

What could be causing only incident data smaller than 1MB to persist while incidents larger than 1MB change to .BAD files?

Options:

A.

A corrupted policy was deployed.

B.

The Enforce server’s hard drive is out of space.

C.

A detection server has excessive filereader restarts.

D.

Tablespace is almost full.