A threat actor sets up a rogue access point (AP) at a local cafe. The rogue AP captures traffic and then forwards the traffic to the cafe AP.
Which type of attack does this scenario describe?
Several employees report that the company intranet website is no longer accepting their login credentials.
You attempt to access the site using its URL and notice several misspellings on the webpage. However, when you access the site directly using its IP address, it functions normally.
What should you do?
A security assessment reveals that a system administrator accessed files outside normal working hours. The assessment identifies the commands executed and records how long the administrator was connected to the system.
Which AAA component does this represent?
An employee accidentally sends an email containing sensitive corporate information to an external email address.
Which type of threat does this scenario describe?
A corporation hires a group of experienced cybercriminals to establish a prolonged and extensive presence within a competitor ' s network. This access will allow the corporation to steal or sabotage sensitive data belonging to its competitor.
Which type of attack does this scenario describe?
A security administrator is implementing defense-in-depth.
Which set of solutions applies protection across different layers of the defense-in-depth approach?
Which encryption type is commonly used to secure WiFi networks?
Which network security technology passively monitors network traffic and compares the captured packet stream with known malicious signatures?
Your supervisor suspects that someone is attempting to gain access to a Windows computer by guessing user account IDs and passwords. The supervisor asks you to use the Windows Event Viewer security logs to verify the attempts.
Which two audit policy events provide information to determine whether someone is using invalid credentials to attempt to log in to the computer? (Choose 2.)
Note: You will receive partial credit for each correct selection.
You are collecting data after a suspected intrusion on the local LAN.
You need to capture incoming IP packets to a file for an investigator to analyze.
Which two tools should you use? (Choose 2.)
Your company is creating a BYOD policy to allow employees to join their personal smartphones to the company network.
Which three requirements are commonly included in a BYOD policy? (Choose 3.)
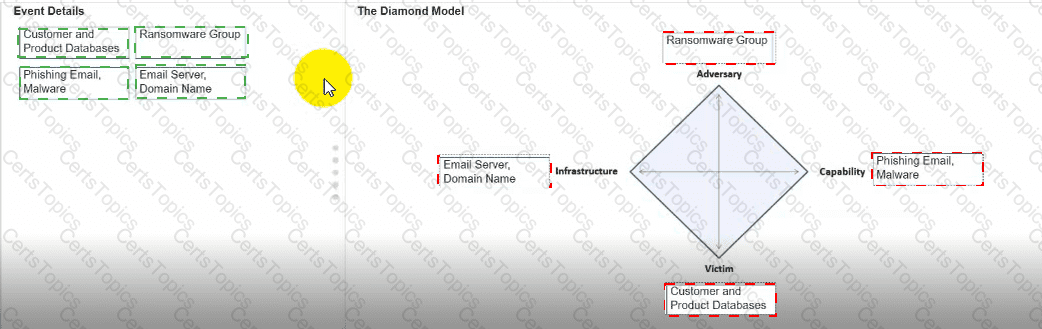
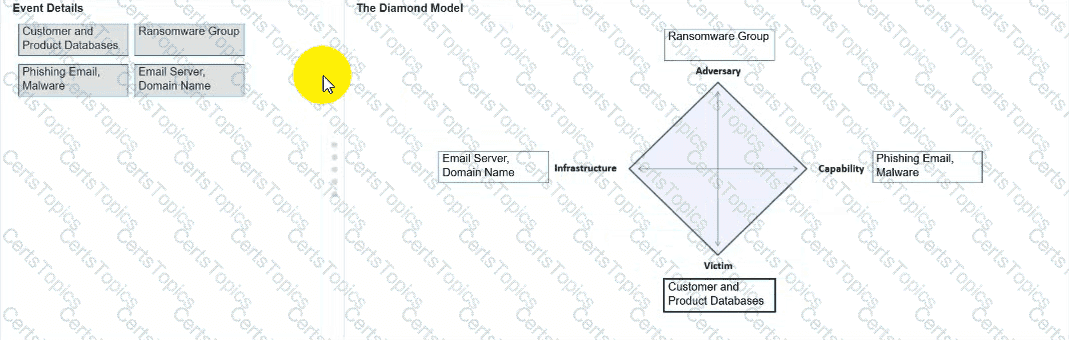
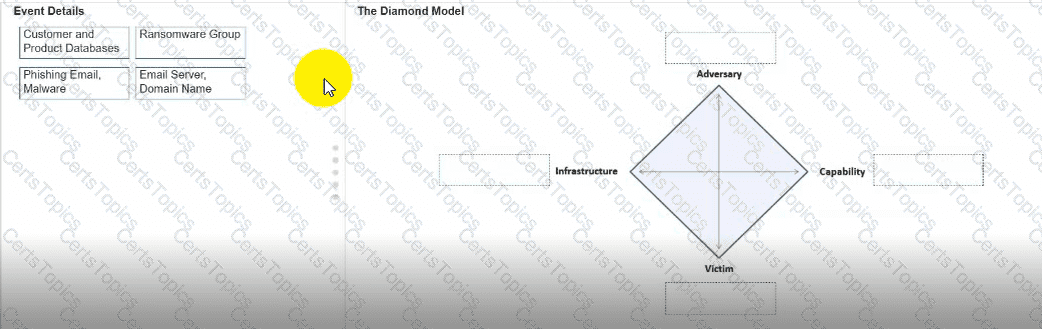
You need to diagram an intrusion event by using the Diamond Model.
Move each event detail from the list on the left to the correct location in the diagram on the right.
Note: You will receive partial credit for each correct response.
You need a software solution that performs the following tasks:
Compiles network data
Logs information from many sources
Provides orchestration in the form of case management
Automates incident response workflows
What product should you use?
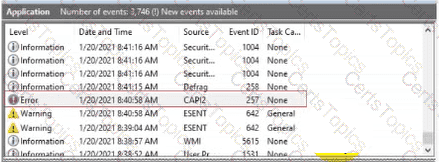
You are reviewing the Application log on a Windows computer. You see an event with an error-level message as shown.
What can you determine about the application that generated the event message?
Which macOS security feature encrypts the entire macOS volume?
How does a honeypot enhance network security?
Which two basic metrics should be taken into consideration when assigning a severity to a vulnerability during an assessment? (Choose 2.)
Which wireless security protocol provides the strongest protection for a home or small business network?
A security assessment showed that a system administrator accessed files outside of normal working hours. The assessment listed the commands the administrator executed and indicated how long the administrator was connected to the system.
Which AAA component does this represent?
Which security assessment of IT systems verifies that PII data is available, accurate, confidential, and accessible only by authorized users?
Copyright © 2021-2026 CertsTopics. All Rights Reserved