What type of attack can CyberArk mitigate?
The ‘LogRetention’ parameter in the DBParm.ini file specifies how long log records are retained.
When are the expired logs cleared?
Customer ACME Corp wants to use the Remote Control Utility for remote administration of the Vaults.
Which default port must be opened from the remote terminal?
What does a SCIM Server refer to?
Where should the Master Private Key be stored?
When Dual Control is enabled for a platform in the Master Policy, exceptions may be configured in the following two locations.
Choose two
A customer needs to implement CyberArk with the lowest possible recovery time objective for a Vault server failure in both the primary and secondary datacenters.
Which architecture is most suitable for this?
In which circumstances is it permissible to install third-party clients on a Vault server?
A customer wants to identify which accounts in CyberArk are past due for a password change.
Which PVWA report would be most suitable for this information?
You need to safeguard secrets used by an application hosted on AWS with Docker. The application has high activity volumes around the clock.
The application accepts customer information and captured images, uploads them to storage, and reads and writes metadata to and from a database service.
Select the option that secures the privileged credentials used in these transactions.
You are deploying PAM for a globally distributed organization with locations in England (UK), Boston (USA), and Hong Kong (ROC).
Each location has two physically separated data centers for disaster mitigation. England DC 1 has been designated as the Primary DC. Components will be scaled horizontally where needed in later phases, and all DCs can communicate with one another.
The solution must provide:
• Resilient access to target systems
• A highly resilient primary location
• Recovery from all locations
• Global resilience to outages
• A single Master Policy governing the solution
Load balancing is possible between DCs in the same region.
What is the minimum required to meet these requirements?
Select the two controls that can be configured at the Master Policy level.
Choose two
A customer has a hybrid infrastructure that spans multiple cloud vendors and privately owned data centers. They deployed CyberArk PAM in AWS by using CyberArk-provided scripts. Eighty percent of the customer’s infrastructure is located in privately owned data centers. The customer is concerned about availability between the cloud provider and the data center. They are cloud-first and are gradually migrating their servers to the cloud.
Active Master Policy settings:
• Require dual-control approval for password access
• Enforce exclusive check-in/check-out access
• Require password changes every 25 days
• Require password verification every 7 days
What is the most appropriate recommendation for the customer?
During phase 1 of the CyberArk Blueprint, what action is recommended for managing service accounts?
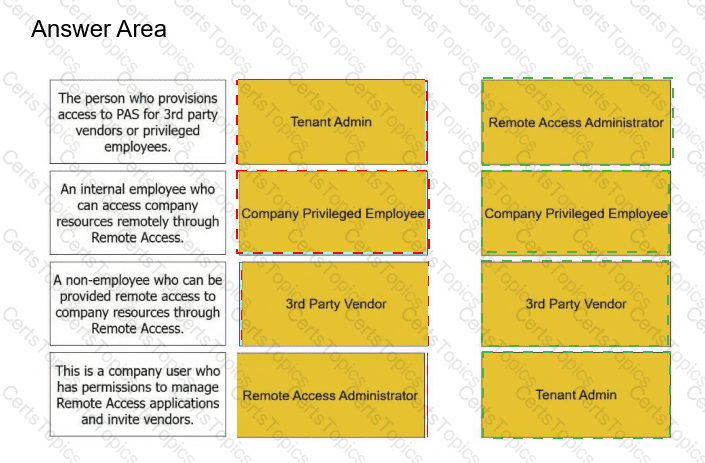
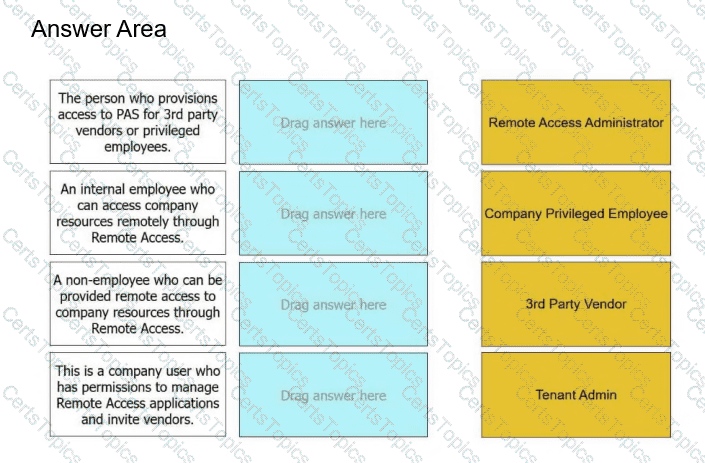
In CyberArk Remote Access, match each persona to its job role:
The organization wants to use a third-party account-discovery tool to add accounts to the Account Feed.
What is the preferred integration method?
What should be the focus of Stage 1 of the CyberArk Blueprint?
Copyright © 2021-2026 CertsTopics. All Rights Reserved